
Kaamos

For EU B2B software teams without a security team.

Pass your security audit without hiring a security team.

Kaamos reads the cloud, identity and code you already run. It finds what isn’t secure, tells you what to fix first, and turns the work into an audit trail.
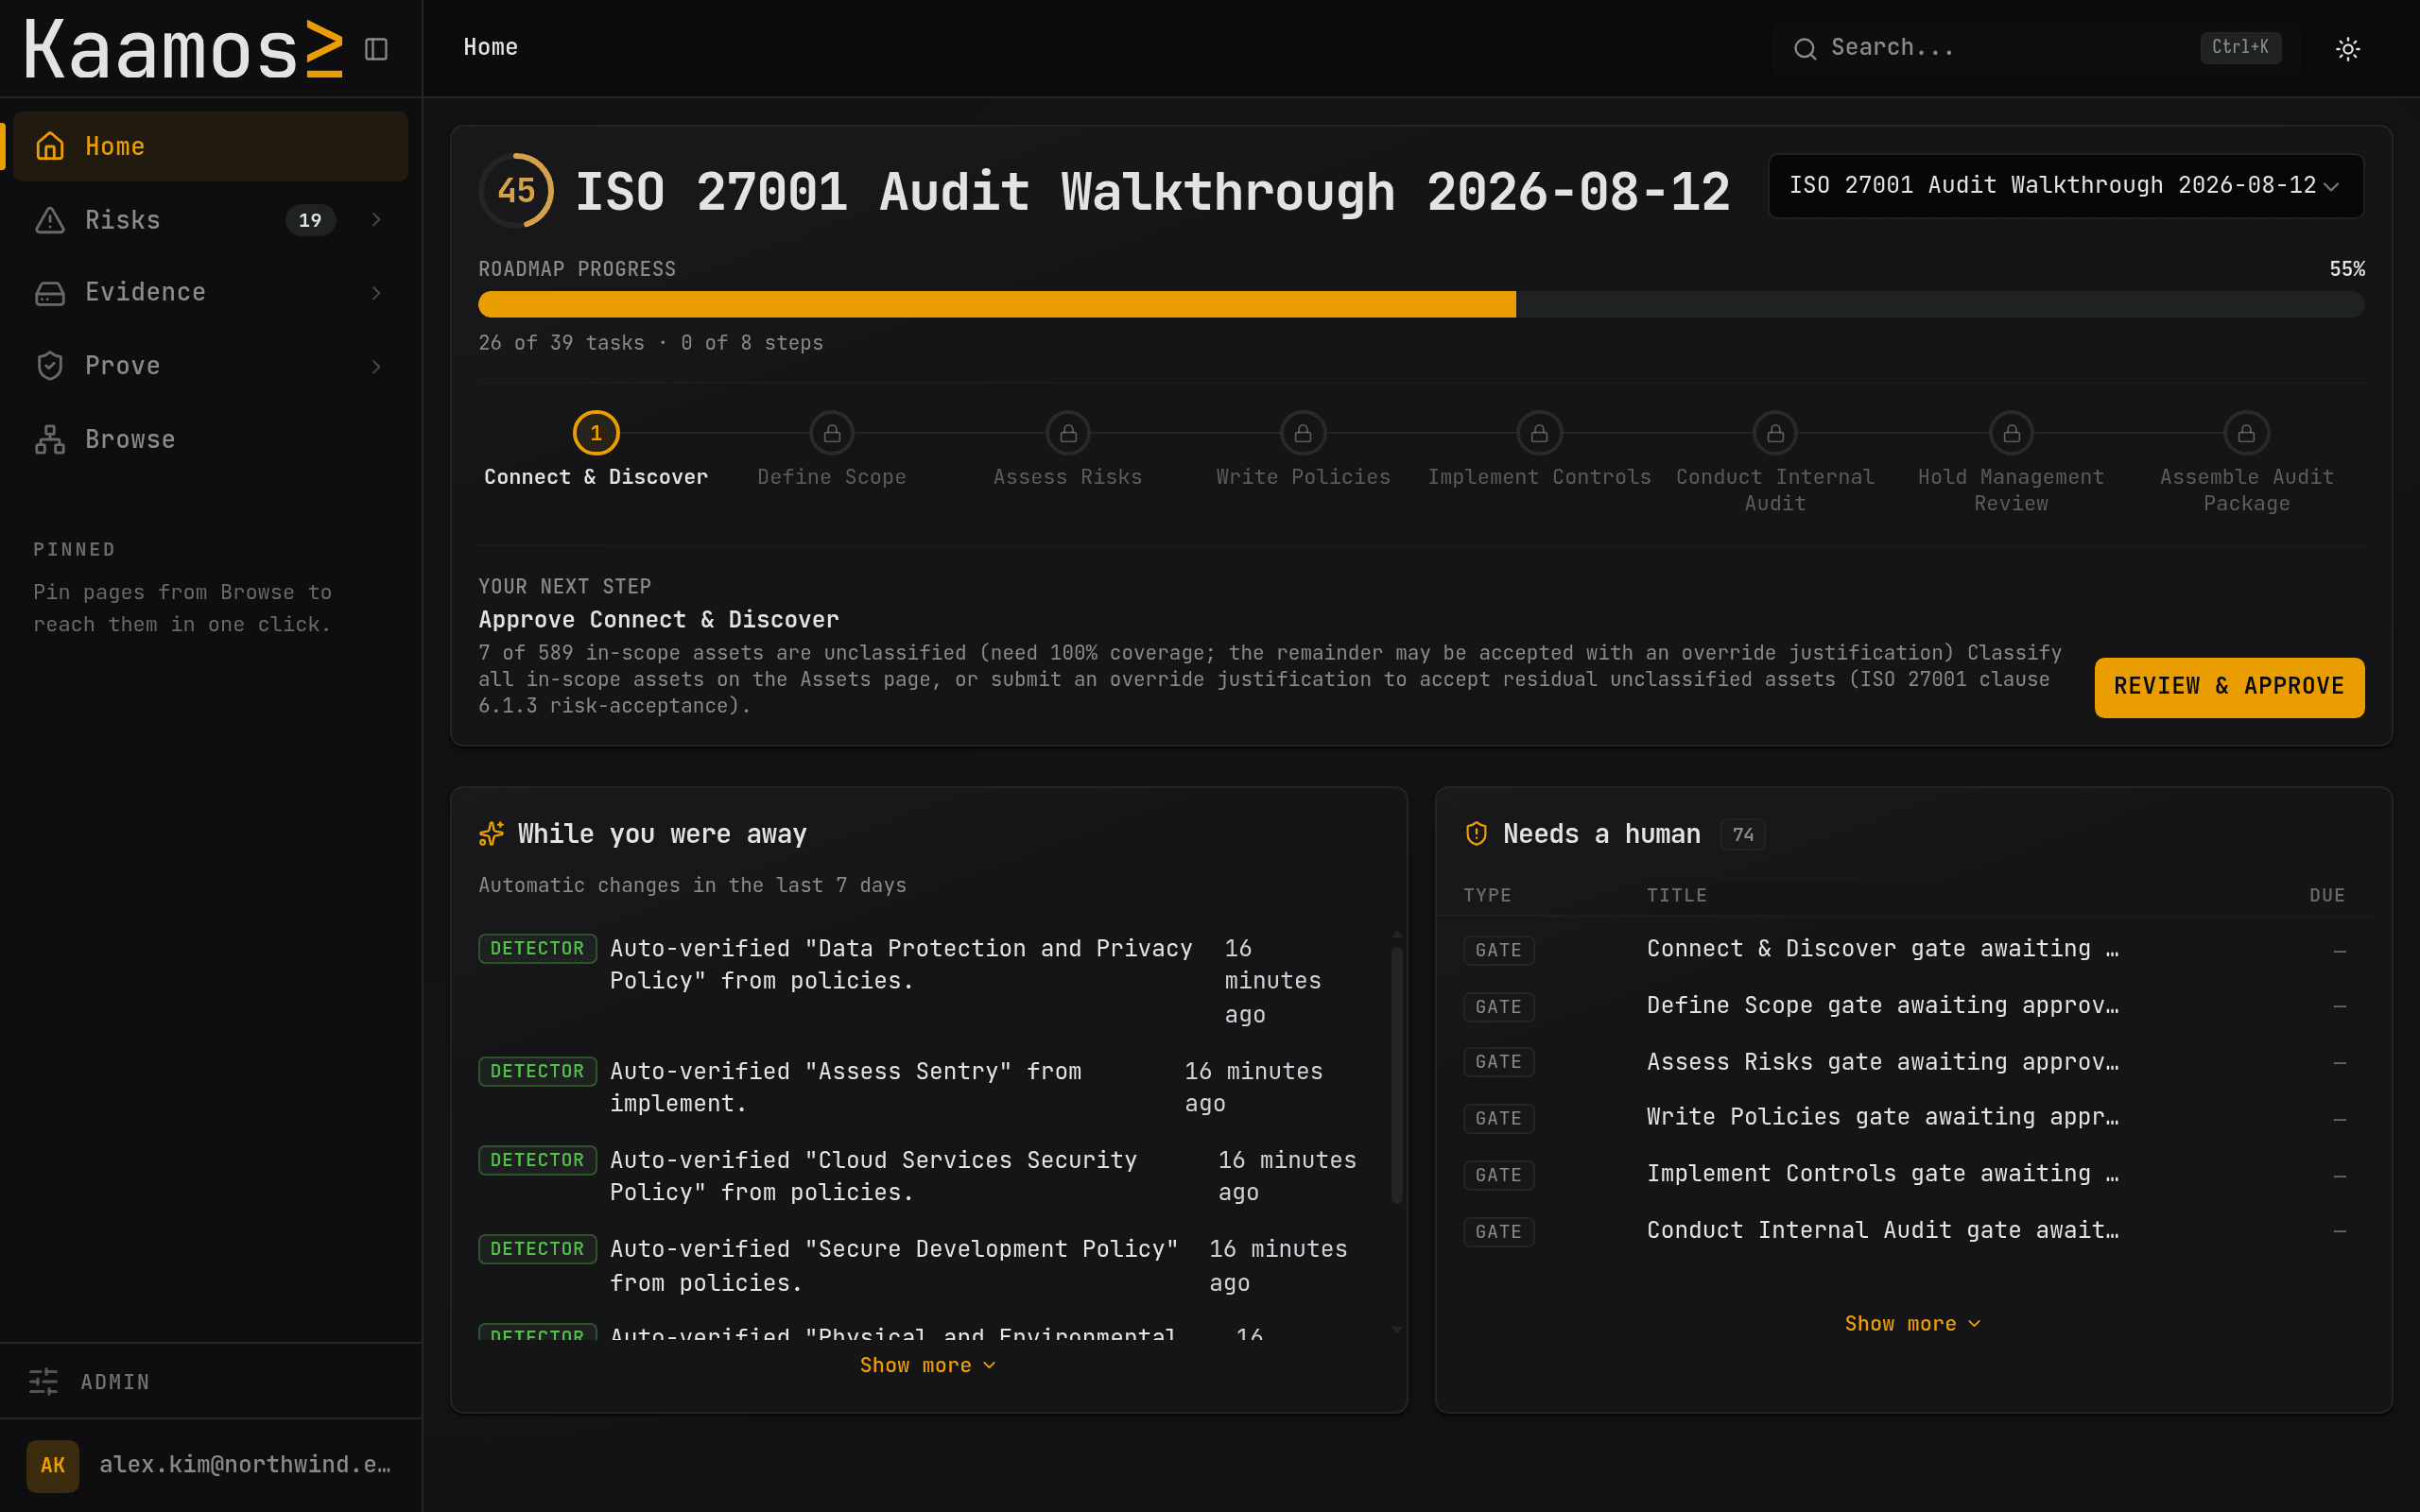
kaamos.ai / home
The Kaamos home screen, showing roadmap progress, automatically verified changes and work waiting for a person.
  • Taiga

01 · What Kaamos does

See what needs attention.
Turn the work into evidence.

One path from the systems you run to the audit you need to pass.
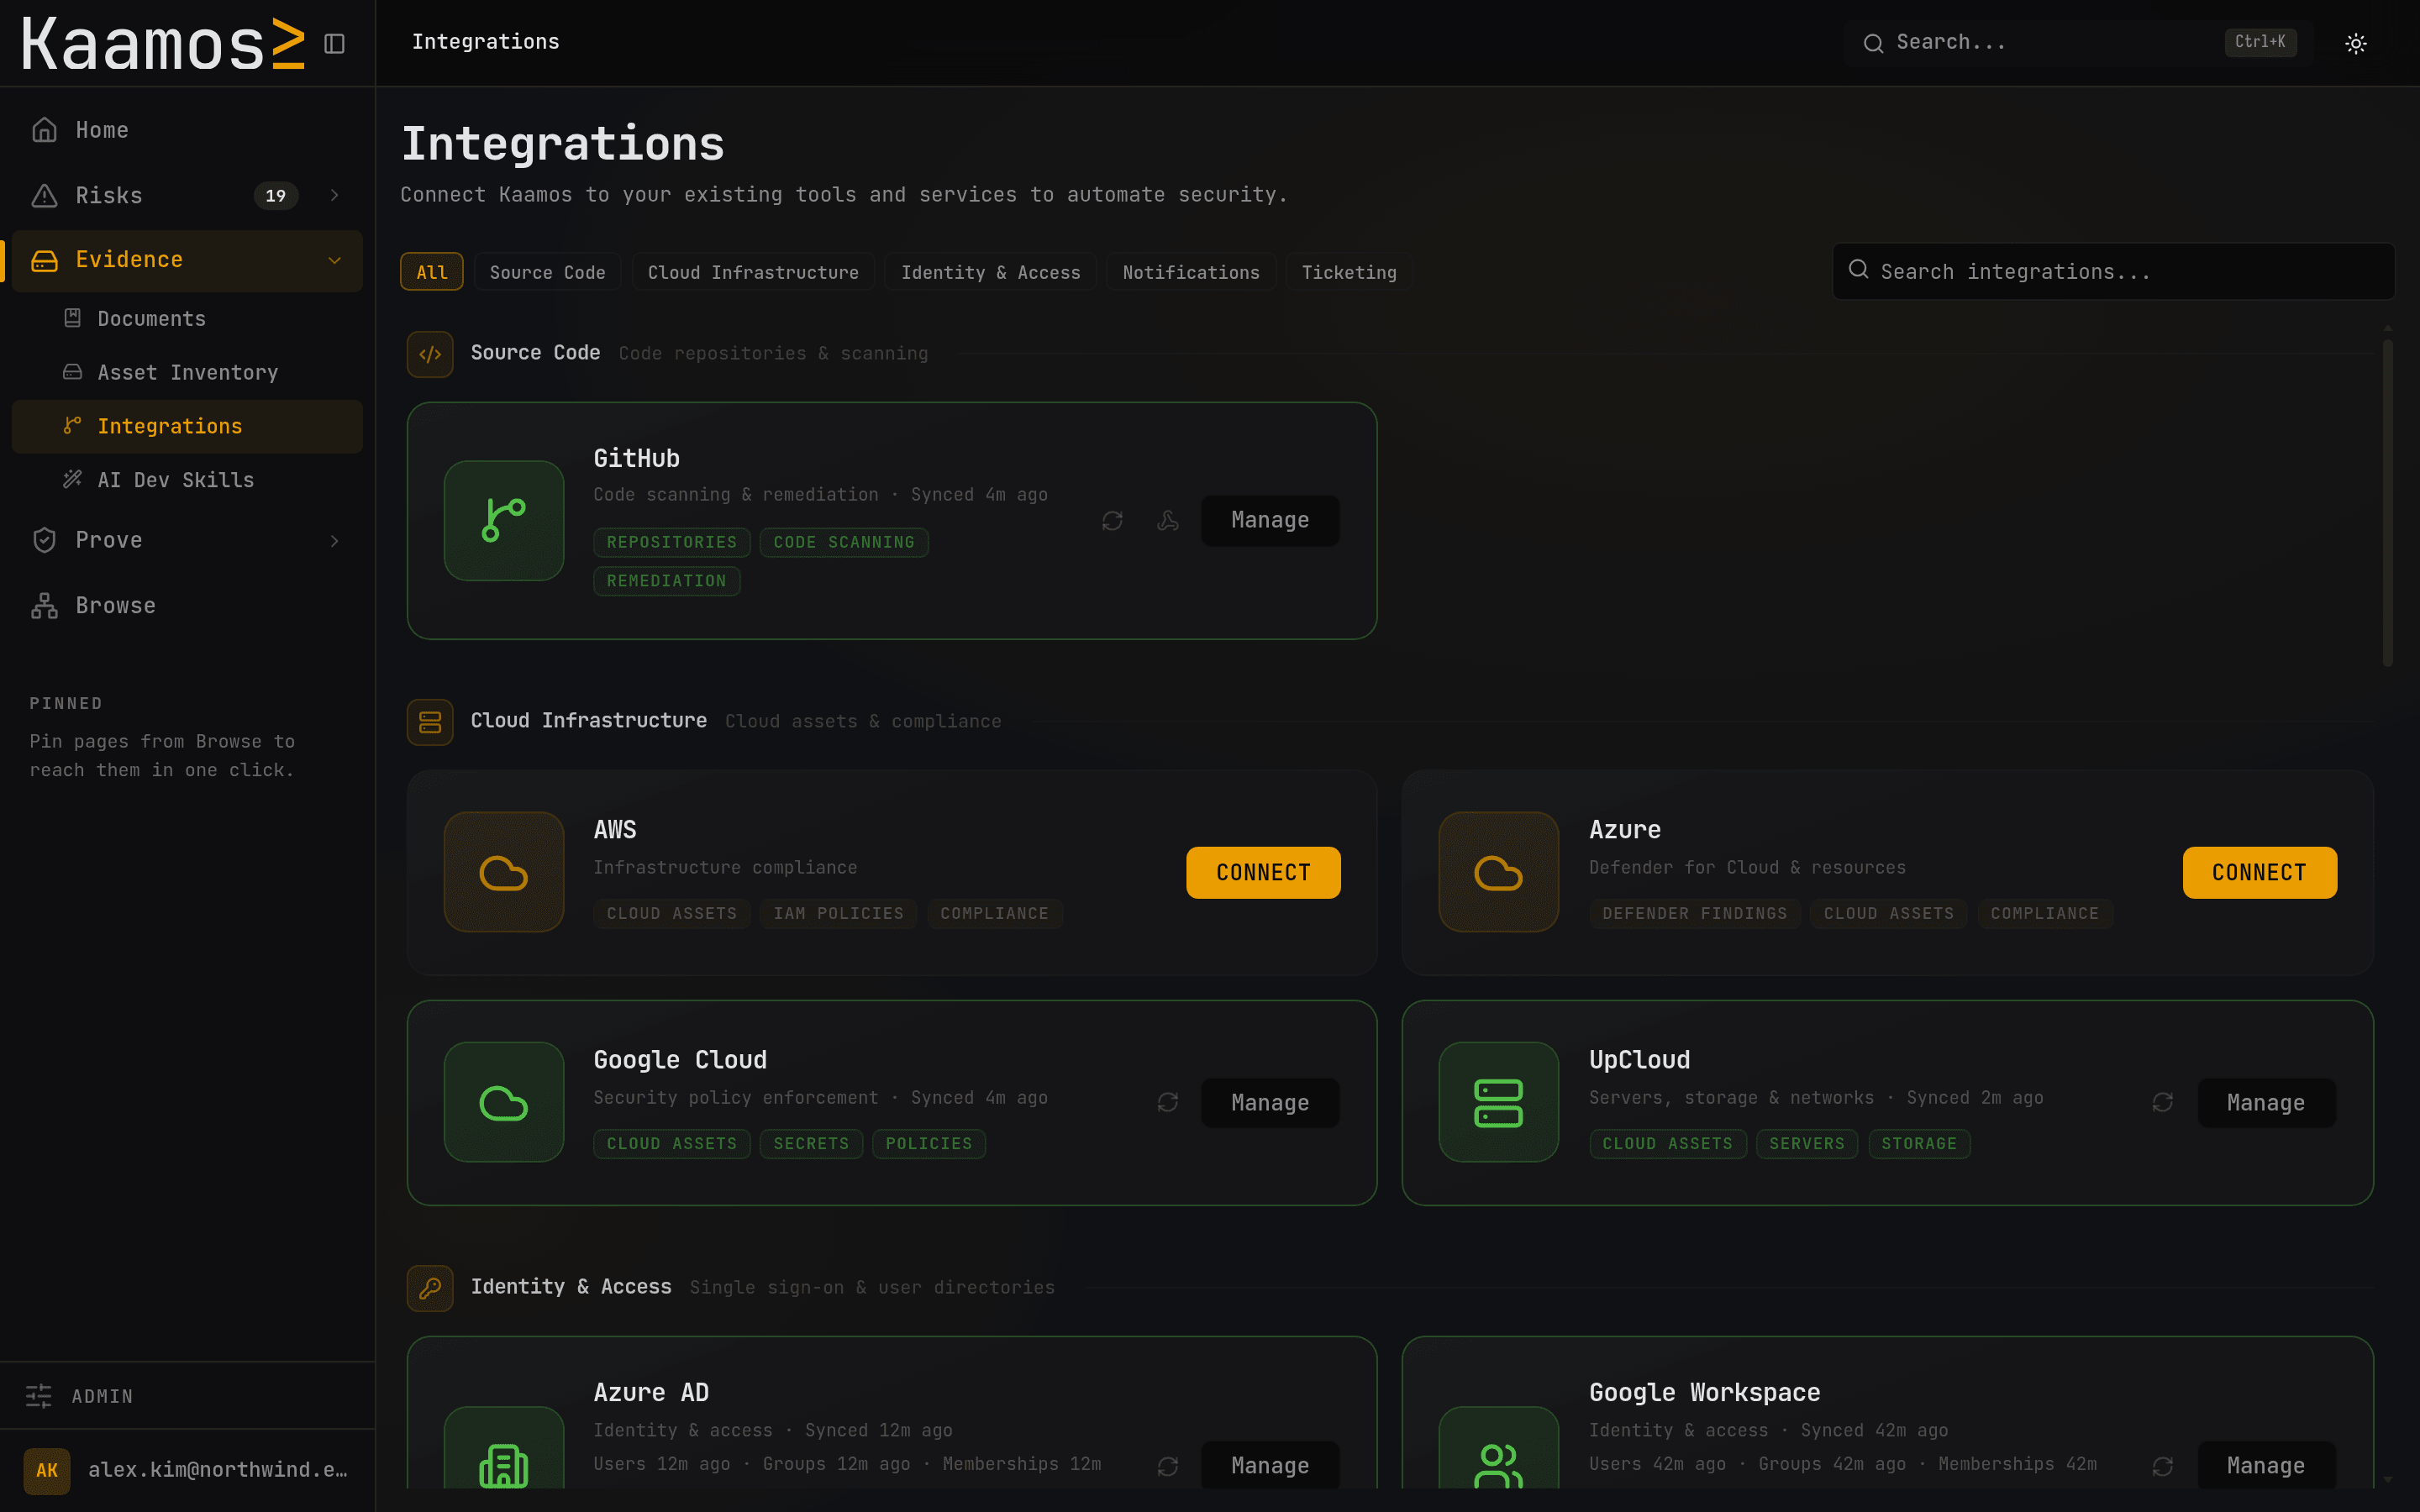
kaamos.ai / integrations
Kaamos integrations: connectors grouped by category, with coverage and last sync information.

Straight from the tools you already use.

02 · Put your agents to work

Your agents do the work.
You make the decisions.

Ask about your environment, draft a policy, or assemble evidence. Your agents work with the same context you see in Kaamos.

Drafts in Kaamos workflows link to their sources.
Proposed changes in Kaamos wait for your approval.

Connect through MCP, the interface your agents use to work with Kaamos. Explore the agent interface ↗

YOUR AGENT + KAAMOS
Your agent

Draft our access control policy, scoped to what we run.

Kaamos

Drafted against your environment and mapped to A.5.15. Waiting for your approval.

InventoryControl mapping
Draft · Awaiting your approval

03 · Evidence you can trace

Every claim has a source.
And a timestamp.

The same systems that reveal the gaps provide the evidence behind the work. Follow the connection.

How evidence flows through KaamosKaamos reads Google Cloud, Google Workspace and GitHub over read-only connections and produces a risk register, controls with evidence attached, an audit-ready evidence pack and an ordered roadmap. Every output names the system it came from and carries a timestamp. Labels are illustrative.CloudGoogle CloudIdentityGoogle WorkspaceCodeGitHubread-onlyKaamos≥Reads · compares · ranksChecked against your systemsRisk registersource · timestampControls with evidencesource · timestampAudit-ready evidencesource · re-read every dayOrdered roadmapnext step · approval waiting
How evidence flows through KaamosKaamos reads Google Cloud, Google Workspace and GitHub over read-only connections and produces a risk register, controls with evidence attached, an audit-ready evidence pack and an ordered roadmap. Every output names the system it came from and carries a timestamp. Labels are illustrative.CloudGoogleCloudIdentityGoogleWorkspaceCodeGitHubread-onlyKaamos≥Reads · compares · ranksChecked against your systemsRisk registersource · timestampControls with evidencesource · timestampAudit-ready evidencesource · re-read every dayOrdered roadmapnext step · approval waiting
Keep it traceable

Connected.

Discovered from your supported connections, not just declared in a questionnaire.

Current.

Re-read from the source, so yesterday’s evidence gets checked.

Traceable.

The system and timestamp are attached. You can check the claim yourself.

Your next step

See where your
security work starts.

Bring your stack and your next audit.
We’ll show you how Kaamos fits.

Book a meeting