Kaamos AI vs Secfix
Compare connected evidence, guided risk assessment and the help included with implementation.
Consider Kaamos AI when
You want an evidence-linked security roadmap and your own agents working across risks, policies and supported actions through MCP.
Secfix may fit when
You want European compliance automation with guided risk assessment, vendor reviews and cloud integrations.
Compare the work and the scope
Framework coverage
Kaamos AI12 supported frameworks, including ISO 27001, SOC 2, GDPR, NIS2, DORA and ISO 42001. Information guides are labeled separately.
See the supported frameworksSecfixSecfix lists ISO 27001, SOC 2, TISAX, GDPR, DORA, NIS2 and ISO 42001 among its frameworks.
Source 1Evidence collection
Kaamos AICloud, identity and code integrations feed inventory and evidence. Review a source record, its collection status and its control links.
See how evidence reaches a controlSecfixIts integration catalog covers cloud, identity and other business tools used for compliance automation.
Source 2Risk and remediation
Kaamos AIA risk register, treatment work and an ordered roadmap keep owners, decisions and evidence connected.
See the risk register and roadmapSecfixGuided questions, risk assessments and mapped controls are documented alongside vendor discovery and security reviews.
Source 1AI and agent workflows
Kaamos AIConnect your agents through MCP to inspect context, propose work and carry out supported actions with your permissions.
See what an agent is allowed to doSecfixSecfix lists CISO AI and AI Questionnaires. Ask to see the specific workflow and review controls you need.
Source 1Package scope
Kaamos AIStartups: 1 framework + GDPR. Growth: 3 + GDPR. Enterprise: unlimited supported frameworks. Core workflows and founder-led onboarding are included.
See what each package includesSecfixRequest the framework scope, implementation responsibilities and ongoing support terms as part of the sales discussion.
Source 1
Bring these questions to both demos.
Use one system, one risk and one target framework. Ask each team to show the work from a source finding to a reviewed result.
- What work does the implementation team do, and what remains with us?
- Which checks are available for our cloud and identity configuration?
- Which AI actions require our review before a change is applied?
Before switching, check evidence exports, policy ownership, integrations and your auditor’s access. Keep your existing records until the new workflow is verified.
Sources & review method
Based on official product, help and package pages, reviewed . Tell us if anything here is out of date and we will re-read it.
Send a correctionWritten by Kaamos AI. This is a review of published capabilities, not an independent benchmark or a test of a customer account. Fit recommendations and demo questions are our judgment. Confirm availability, hosting, support and commercial terms with each vendor.
Other platforms teams weigh against Secfix
Same five questions — framework coverage, evidence, risk, AI workflows and package scope — applied to the rest of the market. Each page cites the vendor's own published pages.
- VantaTrust management and package depthCompare
- DrataCompliance operations and buyer assuranceCompare
- SprintoContinuous monitoring and AI governanceCompare
- SecureframeCompliance automation and advanced riskCompare
- CyberdayISMS collaboration and framework breadthCompare
- KertosPrivacy, security and AI governance togetherCompare
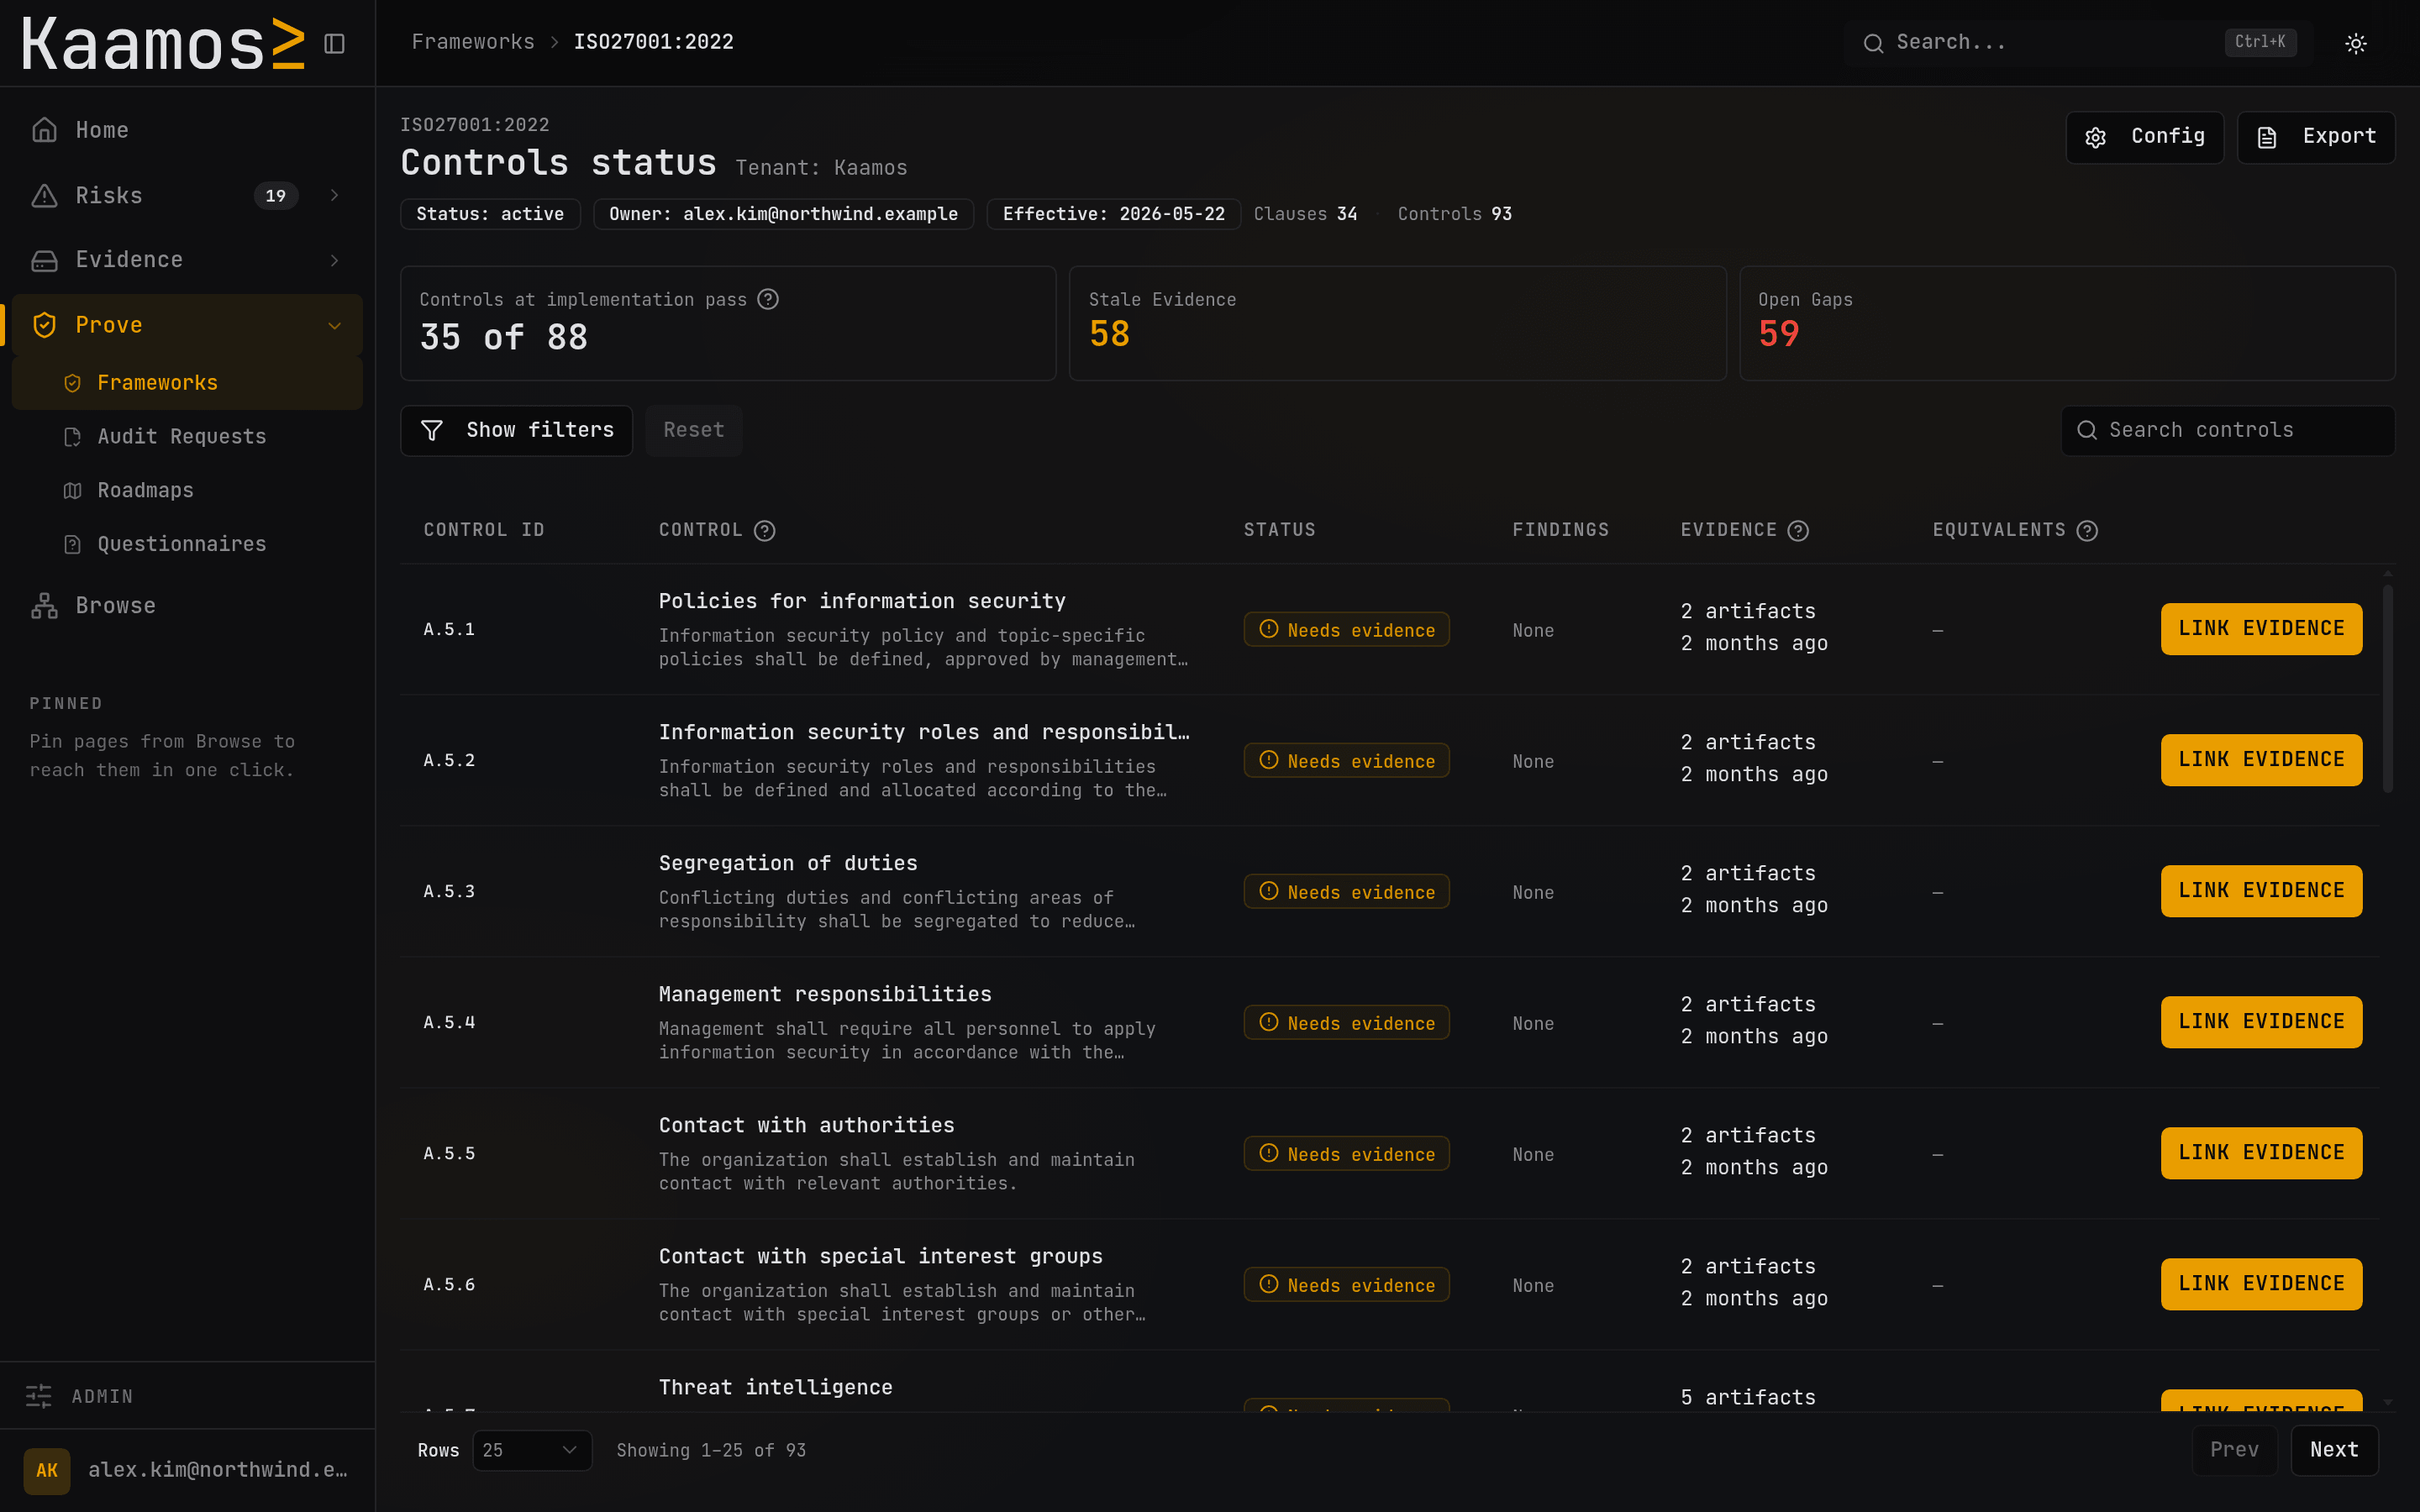
The comparison that decides it runs on your own systems.
Walk through your stack and target framework with a founder, and an honest answer about whether Kaamos is ready for it.