
Kaamos AI vs Sprinto
Compare continuous control monitoring, risk prioritization and AI governance workflows.
Consider Kaamos AI when
You want to connect existing systems, turn findings into an ordered roadmap and let your agents work with the same security context.
Sprinto may fit when
You want automated compliance monitoring together with vendor risk and AI governance in a broader trust program.
Compare the work and the scope
Framework coverage
Kaamos AI12 supported frameworks, including ISO 27001, SOC 2, GDPR, NIS2, DORA and ISO 42001. Information guides are labeled separately.
See the supported frameworksSprintoSprinto presents compliance, vendor risk and AI governance as parts of its trust platform.
Source 1Evidence collection
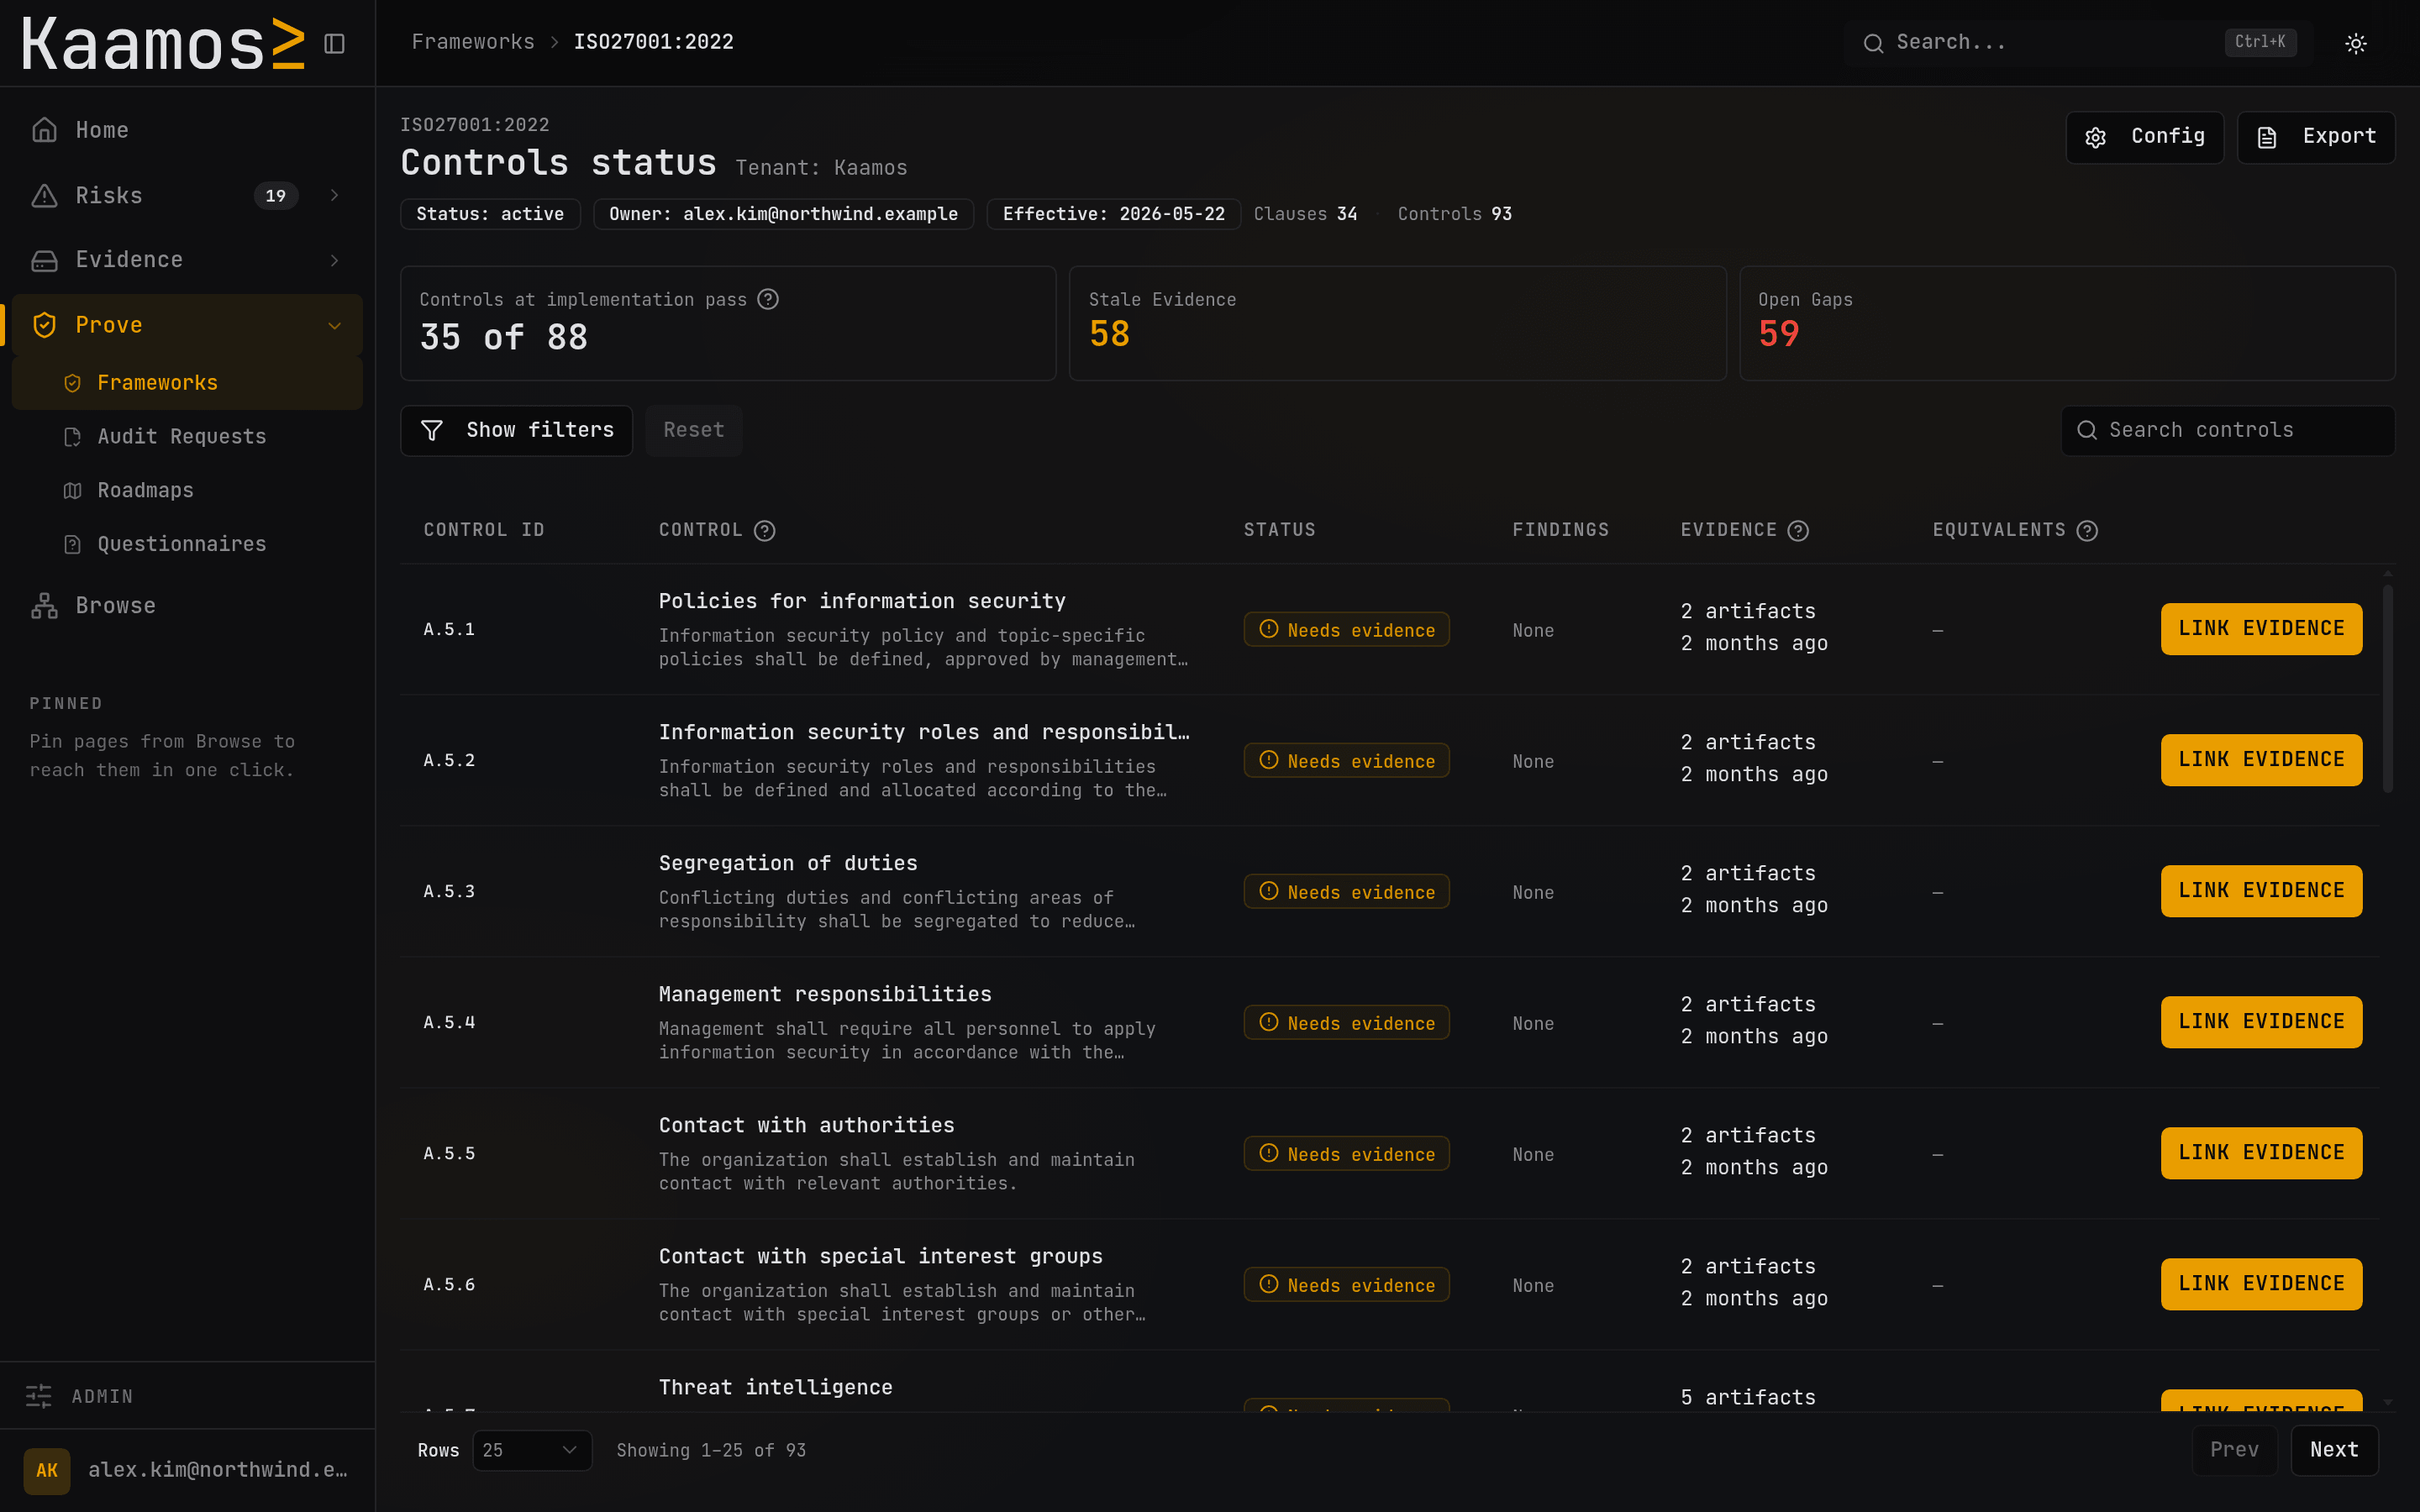
Kaamos AICloud, identity and code integrations feed inventory and evidence. Review a source record, its collection status and its control links.
See how evidence reaches a controlSprintoContinuous monitoring and audit management are part of the platform’s published product scope.
Source 1Risk and remediation
Kaamos AIA risk register, treatment work and an ordered roadmap keep owners, decisions and evidence connected.
See the risk register and roadmapSprintoIts risk product describes live scoring, control mapping and AI assistance using changing security signals.
Source 2AI and agent workflows
Kaamos AIConnect your agents through MCP to inspect context, propose work and carry out supported actions with your permissions.
See what an agent is allowed to doSprintoAI governance covers discovery, risk assessment, approvals and ongoing monitoring of AI tools.
Source 3Package scope
Kaamos AIStartups: 1 framework + GDPR. Growth: 3 + GDPR. Enterprise: unlimited supported frameworks. Core workflows and founder-led onboarding are included.
See what each package includesSprintoConfirm the selected plan, frameworks, governance modules and service scope directly with Sprinto.
Source 1
Bring these questions to both demos.
Use one system, one risk and one target framework. Ask each team to show the work from a source finding to a reviewed result.
- Which AI governance and vendor-risk workflows are included?
- What happens to a control when an integration stops supplying evidence?
- Can we see the proposed plan and usage limits in writing?
Before switching, check evidence exports, policy ownership, integrations and your auditor’s access. Keep your existing records until the new workflow is verified.
Sources & review method
Based on official product, help and package pages, reviewed . Tell us if anything here is out of date and we will re-read it.
Send a correctionWritten by Kaamos AI. This is a review of published capabilities, not an independent benchmark or a test of a customer account. Fit recommendations and demo questions are our judgment. Confirm availability, hosting, support and commercial terms with each vendor.
Other platforms teams weigh against Sprinto
Same five questions — framework coverage, evidence, risk, AI workflows and package scope — applied to the rest of the market. Each page cites the vendor's own published pages.
- VantaTrust management and package depthCompare
- DrataCompliance operations and buyer assuranceCompare
- SecureframeCompliance automation and advanced riskCompare
- CyberdayISMS collaboration and framework breadthCompare
- SecfixEuropean compliance and guided onboardingCompare
- KertosPrivacy, security and AI governance togetherCompare
The comparison that decides it runs on your own systems.
Walk through your stack and target framework with a founder, and an honest answer about whether Kaamos is ready for it.